Guide
The five SOC 2 trust services criteria, and which you need
The SOC 2 trust services criteria are the five areas a report can cover. Only Security is required, so choosing the others carefully is the single biggest lever on cost.
- Preparation, not the examination
- A licensed CPA firm signs the report
- Plain-English guidance
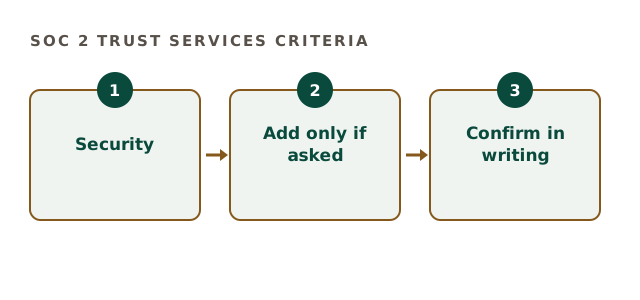
The five SOC 2 trust services criteria
The AICPA defines five criteria, and each covers a different promise to customers. The full text is in the AICPA Trust Services Criteria.
| Criterion | What it covers | Typical cost effect |
|---|---|---|
| Security | Keeping out people who should not be in. | Always required. |
| Availability | The system stays up as promised. | Roughly 10 to 25 percent more. |
| Confidentiality | Sensitive data stays restricted. | Also about 10 to 25 percent. |
| Processing Integrity | Data is processed completely and accurately. | Around 30 to 50 percent. |
| Privacy | Personal data is handled as your notice says. | Also 30 to 50 percent. |
Choosing among the SOC 2 trust services criteria
Ask the customer in writing which criteria they need. Many teams put all five in scope when the customer asked only for Security. As a result, the bill grows for no reason.
Which SOC 2 trust services criteria do you need?
Tick what applies. Each tick may justify one more criterion.
Your result appears here as you tick, so you can see what is still open.
When to add Availability or Confidentiality
Add Availability when you sell an uptime commitment. Similarly, add Confidentiality when contracts promise special handling of sensitive data. Otherwise, Security alone usually satisfies buyers.
Why Privacy is often added by mistake
Privacy sounds essential, so it gets added by default. However, it covers a detailed set of personal-data practices, and it adds significant cost. Therefore add it only when a customer explicitly asks.
Our role
We help you choose the criteria and prepare for them. However, a licensed CPA firm performs the examination, since we are not a CPA firm.
A written answer from the customer protects you later. For example, an email confirming that Security alone is acceptable can be filed with your scope decision. Then, if a different contact asks why Privacy is missing, you can show the agreed scope rather than reopening the whole discussion.
SOC 2 trust services criteria questions
Are all SOC 2 trust services criteria required?
No. Only Security is required, while the others are optional.
Which criteria do most companies choose?
Security alone, sometimes with Availability or Confidentiality.
Can we add criteria later?
Yes. Many companies add one in a later year when a customer asks.
What are the common criteria?
The shared Security controls, numbered CC1 to CC9, which have their own guide.
Related guides
Get the SOC 2 trust services criteria right first
Send us the customer's request. We confirm the criteria and reply with a fixed preparation fee.
Scope your preparation