Guide
SOC 2 requirements: what you actually must have
SOC 2 requirements are less rigid than people fear. The criteria describe outcomes, so you choose controls that fit your company, as long as you can prove they work.
- Preparation, not the examination
- A licensed CPA firm signs the report
- Plain-English guidance
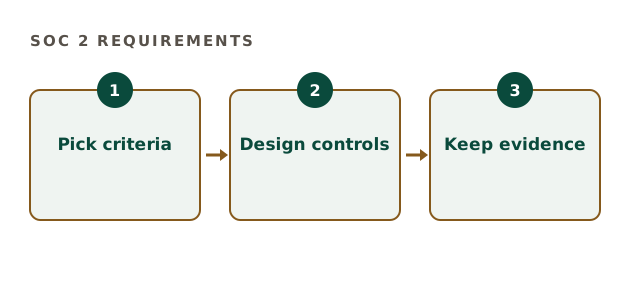
Where SOC 2 requirements come from
The requirements are the AICPA trust services criteria. They do not list tools or settings. Therefore two companies can meet them very differently. The criteria are published in the AICPA Trust Services Criteria.
The controls most companies need
Although the criteria are flexible, most Security-only reports end up with a familiar set.
- Written, approved security policies
- A risk assessment
- Access control with reviews
- Logging, monitoring and incident response
- Change management
- Vendor management
- Backups and recovery
SOC 2 requirements: where do you stand?
Tick what you can show today.
Your result appears here as you tick, so you can see what is still open.
What is not required
Several common assumptions are wrong. So check before spending money.
| Assumption | Reality |
|---|---|
| You need a certificate | No. SOC 2 is an attestation report. |
| You need all five criteria | No. Only Security is required. |
| You need specific tools | No. Controls can use your existing tools. |
| You need an office | No. Remote companies get SOC 2 reports too. |
Evidence is one of the SOC 2 requirements too
A control without proof counts as missing. For example, an access review needs a dated record. Therefore build controls that leave evidence naturally.
Our role
We turn the SOC 2 requirements into a plan that fits your company, then help you close the gaps. However, a licensed CPA firm performs the examination, since we are not one.
A practical way to begin is to list what you already do. Many teams find they meet half the requirements informally, so the work is mostly writing it down and collecting evidence. Then rank the remaining gaps by how likely each is to fail an examination. As a result, effort goes first to the controls that matter most, rather than to the easiest ones. Also schedule recurring controls, such as access reviews, before the watch period begins, because a missed cycle becomes an exception.
SOC 2 requirements questions
Are SOC 2 requirements the same for every company?
The criteria are, but the controls differ by size and stack.
Do we need a compliance platform?
No, although it helps with evidence.
Are SOC 2 requirements a legal obligation?
No. They are a voluntary framework that customers often require.
Do requirements change?
The AICPA updates guidance occasionally, so check the current version.
Related guides
Turn SOC 2 requirements into a plan
Tell us your size and stack. We reply with a written scope and a fixed preparation fee. Every plan lists the controls, the owners and the evidence each one needs, so nothing depends on memory.
Scope your preparation