Guide
How to set SOC 2 scope without paying for what nobody asked
SOC 2 scope decides what the CPA firm examines: which system, which criteria and which supporting teams. So it is the biggest single driver of cost and effort, and it is worth getting right first.
- Preparation, not the examination
- A licensed CPA firm signs the report
- Plain-English guidance
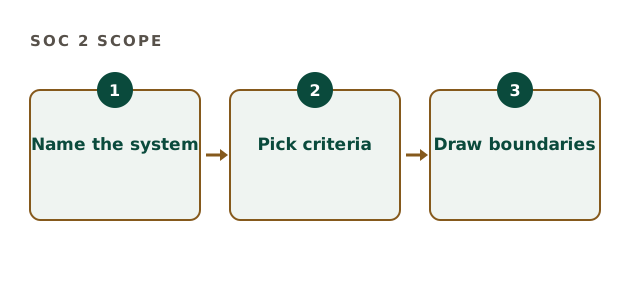
The three parts of SOC 2 scope
Scope has three parts. However, buyers usually care most about the first.
- The system: the product or service customers use
- The criteria: Security, plus any requested extras
- The supporting people, processes and vendors
Choosing the system boundary
Include the production system customers use and the people who run it. Therefore internal tools with no customer data often stay out. Write the boundary down, because fuzzy edges are a top cause of overruns.
SOC 2 scope check
Tick what is decided in writing.
Your result appears here as you tick, so you can see what is still open.
Carve-outs for vendors
Your cloud provider has its own report. So your scope usually carves out its controls and relies on that report instead.
| Method | What it means |
|---|---|
| Carve-out | Vendor controls excluded; you rely on its own report. |
| Inclusive | Vendor controls included in your report. |
How SOC 2 scope affects cost
Each extra criterion adds cost: about 10 to 25 percent for Availability or Confidentiality, and 30 to 50 percent for Processing Integrity or Privacy. Also, each extra system adds testing. So scope to the customer's request.
Our role
We set scope with you in writing before anything else. However, the CPA firm confirms it during planning, because the report is theirs. Criteria: AICPA Trust Services Criteria.
Remember that scope can grow in later years. Starting small is not a weakness, because buyers mainly want to see the system they use covered well. So begin with the product customers buy and the Security criterion. Then expand when a customer asks. Also review the scope each year, since new products or teams may need to join. Writing the scope down clearly each time keeps every renewal predictable for both you and the CPA firm. It also stops scope creep, which is the most common cause of a budget overrun.
SOC 2 scope questions
Can SOC 2 scope be just one product?
Yes. Many companies scope only the product a customer buys.
Does SOC 2 scope include our cloud provider?
Usually it is carved out, relying on the provider's own report.
Can scope grow later?
Yes, in later years, as customers ask.
Who decides scope?
You do, with your consultant, then the CPA firm confirms it.
Related guides
Set your SOC 2 scope before anything else
Send us the customer's request. We reply with a written scope and a fixed preparation fee. The written scope then travels with the engagement letter.
Scope your preparation