Client accountability
You contract with Clearpoint Advisory. One agreement, one fixed fee, one point of contact.
SOC 2 audit preparation
A customer asked for your report and a contract is now waiting. We prepare you for the SOC 2 compliance audit, then an independent licensed CPA firm examines you and issues it. Send four answers and get a written price range back.
Read this first. Clearpoint Advisory is not a CPA firm. We provide SOC 2 readiness, gap analysis, and preparation consulting. The formal SOC 2 examination and report are performed by a separate, licensed, independent CPA firm. We do not perform audits or issue SOC 2 reports.
Four questions, about a minute. No phone number, and no call to book.
Move the sliders. Figures come from published US market data for 2025 and 2026 and stay inside those bands.
An estimate from market ranges, not a quote. Send the same answers through the form and we reply with a scoped range in writing.
Turn this into a real quoteSecurity and engineering teams rely on us for SOC 2 compliance audit preparation without derailing the roadmap.
Logos are the property of their respective owners.
What we do
Confusing those two roles is the most common SOC 2 compliance audit mistake, and it is worth being precise about. Independence rules stop an audit firm from testing controls it designed, so one firm cannot legitimately do both jobs.
We establish which criteria your customer actually requires, then measure you against them. You get a ranked list of what is missing and what would fail first.
Policies written for your real stack, not templates. Access reviews, logging, onboarding, change approvals and vendor records fixed alongside your engineers.
We build the evidence trail the examination will test, then stay in the room while the independent CPA firm runs it and answers get chased down.
Not sure which of these you need?Four answers is enough for us to tell you, in writing.
Find outA SOC 2 compliance audit is an independent examination of how you protect customer data. In a SOC 2 compliance audit a licensed CPA firm looks at your security controls, tests whether they really work, and writes a report saying what it found.
The output of a SOC 2 compliance audit is what your customer wants. They cannot inspect your systems themselves, so instead they ask a neutral third party to do it and to put its name on the answer.
One thing to get straight now. There is no such thing as SOC 2 certification, and no certifying body exists. SOC 2 is an attestation issued by a licensed CPA firm under standards set by the AICPA. Anyone selling you a SOC 2 certificate or badge is selling something your customer’s reviewers will not accept.
Almost nobody goes looking for a SOC 2 compliance audit. It arrives, usually attached to money.
The usual trigger for a SOC 2 compliance audit is a security questionnaire during procurement. A buyer wants proof before they hand over their data, so their vendor review asks for an independent report. Until it appears, the contract sits still.
“No SOC 2 report, no deal” is not a scare tactic. For enterprise buyers it is simply the policy.
Other common triggers for a SOC 2 compliance audit include a compliance deadline, a renewal where the customer raised the bar, or a move upmarket where every prospect starts asking the same question. Some teams also start after a near miss, because a failed vendor review is an unpleasant way to learn the rules.
There are two reports. Buyers frequently ask for a SOC 2 compliance audit without saying which report they mean, so ask them in writing before you spend anything.
| Type I | Type II | |
|---|---|---|
| What it proves | Controls were designed properly on one date. | Controls actually ran properly over months. |
| Watch period | None | 3 to 6 months, and it cannot be skipped |
| Total time | 1 to 3 months | 6 to 12 months |
| Auditor fee | $5,000 to $30,000 | $10,000 to $70,000 |
| Repeats | Rarely, it is usually a stepping stone | Every year |
| Who accepts it | Some buyers, often as a stopgap | Nearly all enterprise buyers |
In short, a Type I SOC 2 compliance audit says the design looks right. A Type II says the design held up under observation. Since a Type II carries a fixed watch window, the calendar rather than the budget decides your finish date.
Still unsure which one your customer will accept?Tell us what they asked for and we will say which report you actually need.
Ask usEvery SOC 2 compliance audit is built on five Trust Services Criteria. Only the first is mandatory. Every extra one you add costs real money, which makes this the highest-stakes decision you will make before starting.
The 40 percent mistake. One unnecessary criterion can widen a SOC 2 compliance audit scope by roughly 40 percent. Before anything else, go back to the customer and get the required criteria in writing.
A SOC 2 compliance audit runs in six stages. Only the last two involve the auditor at all, and the first four are where we work.
Which criteria, which systems, which people. Write down what is excluded too, because vague edges are the main reason budgets drift.
Compare what you do today against what the SOC 2 compliance audit criteria require. The output is a ranked list of what is missing.
Close the gaps. Access reviews, logging, onboarding and offboarding, change approvals, vendor records. This is where most of the effort lives.
Gather the proof a SOC 2 compliance audit needs for every day it should have run. Screenshots, logs, and tickets, not promises.
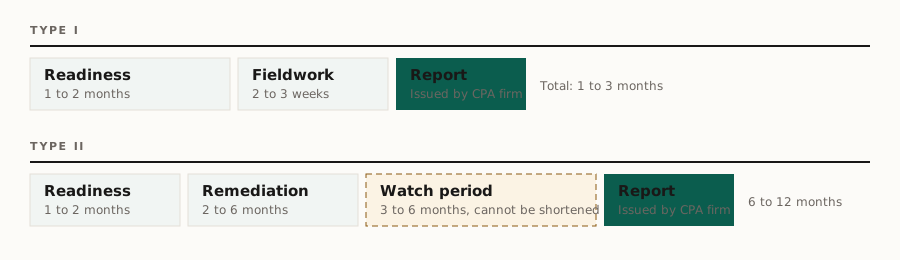
Type II only. Three to six months during which your controls simply operate and the record builds.
Two to four weeks. The licensed CPA firm tests, asks questions, and then issues the report.
A SOC 2 compliance audit produces two separate bills, and confusing them causes most of the sticker shock. Preparation is one cost. The examination itself is another, paid to the CPA firm.
SOC 2 compliance audit pricing varies more than people expect. The same company with the same scope might be quoted roughly $15,000 by a boutique firm, $35,000 by a mid-tier firm, and $90,000 by one of the Big Four. Notably, the premium buys a recognisable logo on the cover rather than a different opinion.
Be careful at the bottom too. A quote of $3,000 to $5,000 for a full examination is a warning sign, because there are not enough hours in it to test anything properly.
Want your number instead of a range?We reply with a scoped fixed fee, usually the same working day.
Get my quoteIn a SOC 2 compliance audit, money buys speed in the preparation phase. Money does not buy speed in the watch period.
| Phase | Type I | Type II |
|---|---|---|
| Readiness and gap analysis | 1 to 2 months | 1 to 2 months |
| Remediation | Usually folded in | 2 to 6 months |
| Watch period | None | 3 to 6 months |
| Fieldwork and reporting | 2 to 3 weeks | 2 to 4 weeks |
| Total | 1 to 3 months | 6 to 12 months |
The watch period is fixed by the standard, so it sets the earliest date your SOC 2 compliance audit can finish. Consequently, the most valuable day to begin is always the first one you seriously consider it.
Only a licensed CPA firm may perform a SOC 2 compliance audit and issue the report. This is not a formality, and it is worth understanding before you hire anyone.
Putting all five in scope when the customer wanted Security alone. Roughly a 40 percent scope increase for nothing.
Policies for systems that turn out to be excluded are wasted work, and they still have to be maintained afterwards.
Evidence automation is genuinely useful. However, it collects proof of controls that exist, and it cannot invent the ones that do not.
Scope creep is the top cause of SOC 2 compliance audit overruns. Write down what is excluded and why, then hold the line.
The SOC 2 compliance audit watch period runs on the calendar, not on urgency. Starting late simply moves your finish date later.
No. SOC 2 produces an attestation report from a licensed CPA firm. No certificate exists and no certifying body exists. Any badge sold as SOC 2 certification will not satisfy a serious vendor review.
No. Independence rules stop an audit firm from testing controls it designed. So if one firm offers to build your controls and then examine them, it is describing something the standard does not permit.
No, although they save time. Those platforms automate evidence collection. Even so, a platform cannot close a gap or draft a policy that matches your architecture, so somebody still has to do that part.
Yes, and plenty of teams do it unaided. It works best when someone internal already knows the criteria and has time to run the project. Otherwise the usual outcome is months of work that the auditor still rejects.
Type II repeats yearly. Afterwards each cycle costs less, because the controls already run and the evidence already collects itself. Meanwhile a bridge letter covers the gap between reports.
About one to three months for a Type I with a small, tidy environment. For a Type II, six months is a genuinely fast result, because the watch period alone runs three to six months.
Quantum Group
Clearpoint Advisory is the SOC 2 audit preparation practice within Quantum Group. We hold the client relationship and stay accountable for the engagement. Specialist and licensed work is carried out by vetted partner firms under contract to us.
You contract with Clearpoint Advisory. One agreement, one fixed fee, one point of contact.
An independent licensed CPA firm performs the examination and issues your report. Always separate from us.
Technical remediation and testing are delivered by partner firms under contract to us, with insurance in place.
Where we are
You contract with Clearpoint Advisory wherever your engagement runs from. The work is delivered remotely across US and UK time zones, so evidence review does not wait on a time difference.
Boston
1 Beacon StreetEastern Time · US engagements
London
169 PiccadillyGreenwich Mean Time · UK and EU engagements
Start here
These four answers are what anyone needs to price a SOC 2 compliance audit properly. That is not a screening exercise, it is genuinely how the work is scoped, and it is why we can quote a range without a call.