Guide
SOC 2 confidentiality: protecting sensitive business data
SOC 2 confidentiality is an optional criterion covering sensitive business information, such as contracts, designs or customer data you promised to restrict. So it suits companies whose contracts make specific confidentiality promises.
- Preparation, not the examination
- A licensed CPA firm signs the report
- Plain-English guidance
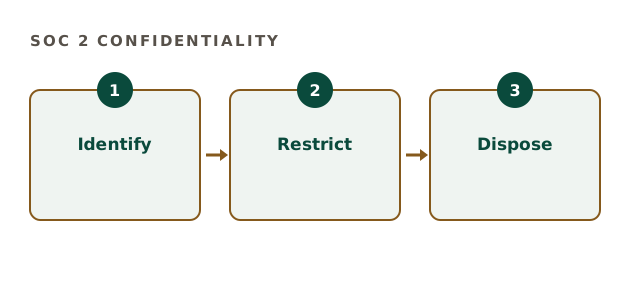
What SOC 2 confidentiality covers
The criterion asks you to identify confidential information, protect it and dispose of it as agreed. Therefore the CPA firm looks for classification, access restriction and disposal records. The text is in the AICPA Trust Services Criteria.
The controls it usually adds
Most companies already do part of this. However, the criterion requires evidence for each step.
- A data classification scheme
- Access limited to those who need it
- Retention periods stated in policy
- Secure disposal with records
- Confidentiality terms with staff and vendors
Do you need SOC 2 confidentiality?
Tick what applies. Several ticks suggest adding it.
Your result appears here as you tick, so you can see what is still open.
SOC 2 confidentiality compared with Security alone
Security already restricts access. So the added work is mostly classification and disposal.
| Area | Security only | With Confidentiality |
|---|---|---|
| Access control | Required. | Required, plus need-to-know rules. |
| Classification | Optional. | Required. |
| Disposal | Optional. | Required, with records. |
| Cost effect | Baseline. | Roughly 10 to 25 percent more. |
When to add SOC 2 confidentiality
Add it when customers or contracts expect specific handling of their sensitive data. For example, firms handling legal documents or product designs often need it. Otherwise, Security alone usually satisfies buyers.
Our role
We help design classification and disposal controls that fit your size. However, the examination is performed by a licensed CPA firm, because we are not one.
Disposal is where most teams have gaps. For example, data left in old backups, test environments or departed employees' laptops is still data you promised to restrict. So list where confidential data can end up, then decide how each copy is removed. Also keep simple disposal records, such as a ticket when a dataset is deleted. That evidence is usually what the CPA firm samples, and it is easy to collect once the habit exists. So build the habit before the watch period begins.
SOC 2 confidentiality questions
Is SOC 2 confidentiality the same as Privacy?
No. Confidentiality protects business information, while Privacy protects personal information.
How much does it add?
Roughly 10 to 25 percent to the examination.
Does SOC 2 confidentiality need encryption?
Encryption helps, but classification and disposal are the core.
Can we add it later?
Yes, when a customer asks.
Related guides
Scope Confidentiality only if it earns its cost
Send us the customer's request. We confirm the scope and quote a fixed preparation fee. We also flag where Security alone would already satisfy the customer, so you avoid paying for an unneeded criterion.
Scope your preparation