Guide
SOC 2 privacy criteria: what they add, and when you need them
The SOC 2 privacy criteria cover how you collect, use, keep and dispose of personal information. They sound essential. However, they add real cost, so add them only when a customer asks.
- Preparation, not the examination
- A licensed CPA firm signs the report
- Plain-English guidance
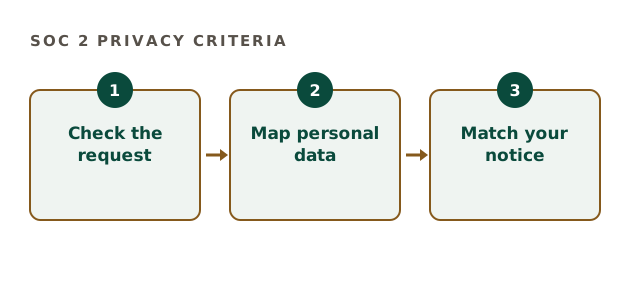
What the SOC 2 privacy criteria cover
The privacy criteria test whether you handle personal information the way your privacy notice says. So they cover notice, choice, collection, use, retention, disclosure, quality and monitoring. The full text is in the AICPA Trust Services Criteria.
Privacy versus Confidentiality
People often confuse the two. However, they protect different things.
| Confidentiality | Privacy | |
|---|---|---|
| Protects | Sensitive business information. | Personal information about individuals. |
| Main test | Restricted access and disposal. | Handling matches the privacy notice. |
| Cost effect | About 10 to 25 percent more. | About 30 to 50 percent more. |
Do you need the SOC 2 privacy criteria?
Tick what applies. Two or more ticks may justify adding Privacy.
Your result appears here as you tick, so you can see what is still open.
Why the SOC 2 privacy criteria cost more
They require detailed processes, such as handling access requests and tracking consent. Also, the CPA firm must test each one. Therefore Privacy is one of the most expensive additions.
When to add the SOC 2 privacy criteria
Add them when a customer explicitly asks, usually because you process consumer data on their behalf. Otherwise, Security plus a strong privacy programme outside the report often satisfies buyers.
- A customer asked for Privacy in writing
- You process consumer personal data at scale
- Your contracts promise specific privacy practices
Our role
We help you decide, and then prepare the controls if Privacy is in scope. However, the examination is performed by a licensed CPA firm, since we are not one.
If you are unsure, start without Privacy and revisit it next cycle. Meanwhile, keep your privacy notice accurate and your data inventory current, because those are the foundations the criteria would test. As a result, adding Privacy later becomes a smaller step, and you avoid paying for it before any customer asks. Also record the decision and the reason, so the choice is easy to explain if a buyer asks.
SOC 2 privacy criteria questions
Are the SOC 2 privacy criteria the same as GDPR?
No. They overlap with privacy laws, but they are a separate framework.
Can we add Privacy later?
Yes. Many companies add it in a later cycle when a customer asks.
Do the SOC 2 privacy criteria replace a privacy programme?
No. They test the programme you already run.
Why is Privacy added by mistake?
Because it sounds essential, although most buyers ask only for Security.
Related guides
Decide on Privacy before you scope
Send us the customer's request. We confirm whether Privacy is needed, then quote a fixed preparation fee.
Scope your preparation