Guide
The SOC 2 common criteria, CC1 to CC9, in plain words
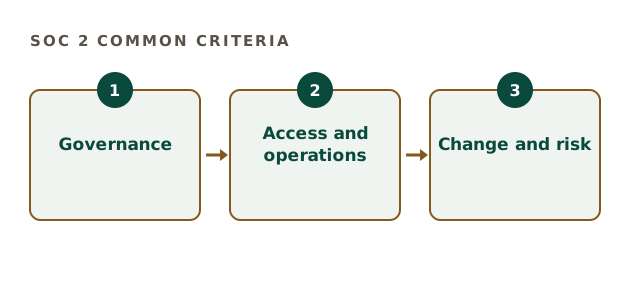
The SOC 2 common criteria are the Security controls every report includes. So whatever else you add, these nine groups form the backbone of your examination.
- Preparation, not the examination
- A licensed CPA firm signs the report
- Plain-English guidance
Why they are called the SOC 2 common criteria
They are common because they apply to every criterion. For example, access control protects Availability and Confidentiality as much as Security. Therefore they appear in every SOC 2 report. The text is in the AICPA Trust Services Criteria.
The nine groups
Each group covers one part of how you run security.
| Group | Plain meaning |
|---|---|
| CC1 Control environment | Leadership, ethics and roles. |
| CC2 Communication | Policies are shared and understood. |
| CC3 Risk assessment | Risks are identified and analysed. |
| CC4 Monitoring | Controls are checked over time. |
| CC5 Control activities | Policies and procedures exist. |
| CC6 Access | Only authorised people get in. |
| CC7 Operations | Incidents are detected and handled. |
| CC8 Change | Changes are approved and tested. |
| CC9 Risk mitigation | Vendors and disruptions are managed. |
SOC 2 common criteria coverage check
Tick each group you could evidence today.
Your result appears here as you tick, so you can see what is still open.
Where the SOC 2 common criteria find exceptions
Most exceptions land in CC6 and CC8, because access and change happen daily. Also, CC3 is often missing entirely. So prioritise those three when preparing.
Meeting the SOC 2 common criteria at small scale
A small team meets the same criteria with lighter controls. For example, a five-person company can meet CC1 with a short org chart and defined roles. However, every control still needs evidence.
Our role
We map your existing practices to each group, then close the gaps. We are not a CPA firm, so the examination is performed separately by a licensed firm.
It also helps to map existing practices before writing anything new. For example, an onboarding checklist may already cover parts of CC1, CC2 and CC6. Therefore the real gap is often evidence, not process. Start by listing what you already do, then mark what leaves a record and what does not. That list becomes the plan for closing the gaps without building duplicate processes.
SOC 2 common criteria questions
Are the SOC 2 common criteria the same as the Security criterion?
Yes, in practice. Security is defined by the common criteria.
How many controls map to them?
Often 60 to 120, depending on how a company groups its controls.
Which SOC 2 common criteria fail most often?
CC6 access, CC8 change and a missing CC3 risk assessment.
Do extra criteria add to these?
Yes. Each extra criterion adds its own requirements on top.
Related guides
Close the gaps across all nine groups
Tell us your size and stack. We reply with a written scope and a fixed preparation fee.
Scope your preparation