Guide
What is inside a SOC 2 report, section by section
A SOC 2 report is the document your customer actually reads. So it helps to know its sections, because buyers skim certain parts first and judge you on them.
- Preparation, not the examination
- A licensed CPA firm signs the report
- Plain-English guidance
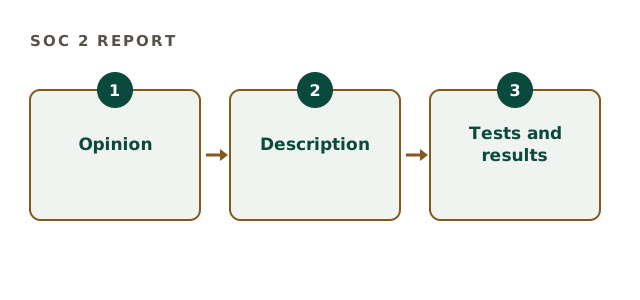
The main sections of a SOC 2 report
Most reports follow the same structure. However, length varies widely with scope.
- The CPA firm's opinion
- Management's assertion
- The system description
- Controls mapped to criteria
- Tests performed and results, in a Type 2
The opinion comes first
Buyers read the opinion before anything else. An unqualified opinion means the CPA firm found the controls suitably designed, and in a Type 2 also operating effectively. A qualified opinion, by contrast, flags a material problem, so it triggers questions.
SOC 2 report readiness: will yours read well?
Tick what you expect your report to show.
Your result appears here as you tick, so you can see what is still open.
How buyers read exceptions in a SOC 2 report
Exceptions are individual test failures. Therefore a few exceptions with clear management responses rarely kill a deal, while a pattern does.
| Section | What buyers look for |
|---|---|
| Opinion | Unqualified or qualified. |
| Description | Whether their data is in scope. |
| Exceptions | How many, and management's response. |
| User entity controls | Duties you expect them to perform. |
Complementary user entity controls
Every report lists duties the customer must perform, such as managing their own user access. So read that section yourself too, because customers will ask about it.
Who issues a SOC 2 report
Only a licensed CPA firm can issue it, under AICPA standards. We are not a CPA firm, so we prepare you for the examination. There is no SOC 2 certificate. Reference: AICPA guidance on SOC 2.
It also helps to read a few reports from your own vendors before yours is written. For example, your cloud provider's report shows how a mature system description reads. As a result, you will know what a good description looks like, and you can brief your team accordingly. That small step often makes the first draft much closer to final.
SOC 2 report questions
How long is a SOC 2 report?
Often 40 to over 100 pages, depending on scope.
Who can see our SOC 2 report?
Usually customers and prospects under NDA, because it contains detail.
How long is a SOC 2 report valid?
Buyers usually expect one covering the last twelve months, so it repeats yearly.
Can exceptions be fixed after the report?
They stay in that report, but the next one can show them fixed.
Related guides
Prepare for a SOC 2 report that reads well
Tell us your scope and timeline. We reply with a written scope and a fixed preparation fee.
Scope your preparation