Guide
SOC 2 and NIST: a report and a framework, and how they connect
SOC 2 and NIST are often mentioned together. However, one is an attestation report issued by a CPA firm, while the other is a set of frameworks you can adopt.
- Preparation, not the examination
- A licensed CPA firm signs the report
- Plain-English guidance
How SOC 2 and NIST differ
SOC 2 produces a report for customers. In contrast, NIST publishes frameworks and controls, such as the Cybersecurity Framework and SP 800-53. Therefore nobody issues a general NIST report in the way a CPA firm issues SOC 2.
| Topic | SOC 2 | NIST |
|---|---|---|
| Type | Attestation report | Frameworks and control catalogues |
| Issued by | Licensed CPA firm | Not issued, adopted |
| Common use | Commercial customers | Government and regulated sectors, and many others |
Mapping SOC 2 and NIST controls
The control areas overlap heavily. For example, access control, logging and incident response appear in both. Also, the AICPA publishes mappings between its criteria and NIST frameworks.
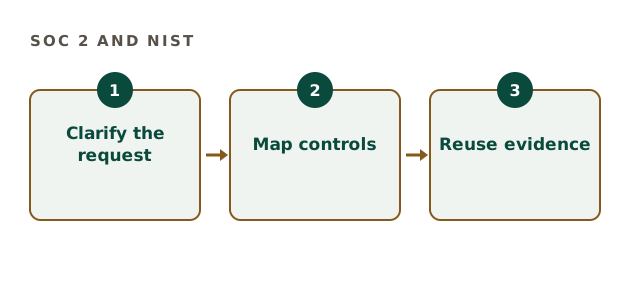
So one control set can serve both, with mapping kept in a single document.
SOC 2 and NIST planning check
Tick what you know about the request.
Your result appears here as you tick, so you can see what is still open.
When buyers ask for SOC 2 and NIST
Federal or regulated buyers may cite NIST. Meanwhile, commercial buyers usually ask for SOC 2.
- Ask exactly what evidence the buyer wants
- Check whether a SOC 2 report plus a mapping satisfies them
- Note any formal programme they require, such as FedRAMP
- Avoid building two separate control sets
Reusing evidence
Evidence collected for SOC 2 often supports NIST alignment. Therefore tag evidence by control, not by framework. As a result, new requests take days rather than months.
In addition, keep the mapping current when controls change.
Where Clearpoint helps
We prepare SOC 2 controls and map them to NIST where buyers ask. Our preparation fee is fixed, between $5,000 and $40,000. We are not a CPA firm. NIST material is on the NIST Cybersecurity Framework page.
Also watch the language in contracts. For example, a clause requiring alignment with a NIST framework differs from one requiring a formal programme. So legal and security teams should read requirements together. In addition, record how you answered each buyer, because the same question will return.
SOC 2 and NIST questions
Can one programme cover SOC 2 and NIST?
Yes. One control set with a mapping often serves both.
Is there a NIST certificate like a SOC 2 and NIST report pair?
No. NIST frameworks are adopted, not certified by NIST.
Which matters more, SOC 2 and NIST alignment or FedRAMP?
FedRAMP is a formal programme for federal cloud services, so it is separate.
Does the AICPA map its criteria to NIST?
Yes, it publishes mapping documents.
Related guides
Align SOC 2 and NIST without duplicate work
Tell us what your buyers asked for. We reply with a written scope and a fixed preparation fee.
Scope your preparation