Guide
Cloudflare SOC2: using their report in your vendor review
Cloudflare SOC2 documentation helps when Cloudflare sits in front of your application. So it belongs in your vendor file, alongside evidence of how you configured it.
- Preparation, not the examination
- A licensed CPA firm signs the report
- Plain-English guidance
Why Cloudflare SOC2 evidence matters
Traffic to your product may pass through Cloudflare. Therefore auditors may treat it as a key vendor, and your vendor review should cover it.
Cloudflare provides compliance documentation to customers. Also, its compliance resources list the reports and programmes it maintains.
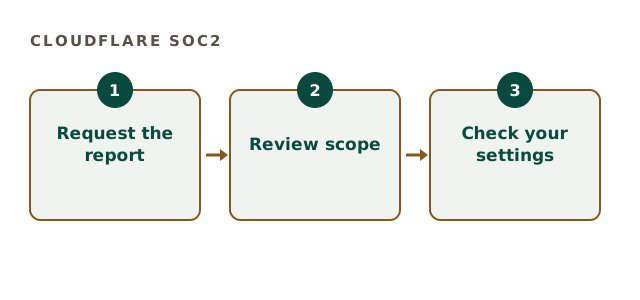
Reviewing the Cloudflare SOC2 report
Read it like any vendor report. However, pay attention to which products are covered.
- Products and services in scope
- Report period and opinion
- User entity controls
- Subservice organisations and carve-outs
- Exceptions and responses
Cloudflare SOC2 review check
Tick what your vendor file holds.
Your result appears here as you tick, so you can see what is still open.
Your side of Cloudflare SOC2 scope
Account configuration remains yours. For example, who can change firewall rules or DNS records.
| Area | Your evidence |
|---|---|
| Account access | Members, roles and MFA |
| Configuration changes | Audit logs and approvals |
| API tokens | Inventory with scoped permissions |
| Certificates and TLS | Settings and renewal monitoring |
Filing the review
Keep the report, a short review note and the date together. So the CPA firm sees that vendor monitoring happened. As a result, the evidence takes minutes to produce.
In addition, schedule the next review when a new report is expected.
Where Clearpoint helps
We build your vendor review routine and bring key configuration into your control set. Our preparation fee is fixed, between $5,000 and $40,000. We are not a CPA firm. Cloudflare's documents are listed on its Cloudflare compliance resources page.
Also limit who can change security settings. Because firewall rules and DNS records protect your product, broad account roles create risk. So assign the narrowest roles that work, and review them periodically. In addition, export audit logs on a schedule, because they show who changed what. As a result, your configuration evidence matches the controls in your system description.
Cloudflare SOC2 questions
How do we get the Cloudflare SOC2 report?
Customers can obtain it through Cloudflare's compliance documentation.
Does Cloudflare SOC2 coverage include our settings?
No. Your account configuration remains your responsibility.
Is Cloudflare SOC2 review needed every year?
Yes, when each new report is issued.
Is Cloudflare a subservice organisation for us?
It depends on your system description, so discuss it with your CPA firm.
Related guides
File your Cloudflare SOC2 review properly
Tell us which vendors sit in your stack. We reply with a written scope and a fixed preparation fee. Also mention which Cloudflare products you use, because coverage differs by product.
Scope your preparation