Comparison
SOC 1 vs SOC 2: which report is your customer asking for?
The choice between SOC 1 vs SOC 2 depends on what your customer worries about. SOC 1 covers controls that affect their financial statements, while SOC 2 covers how you protect their data.
- Preparation, not the examination
- A licensed CPA firm signs the report
- Plain-English guidance
The core difference in SOC 1 vs SOC 2
A SOC 1 report helps your customer's financial auditors. So it suits services such as payroll, billing or claims processing. A SOC 2 report, by contrast, helps security and procurement teams decide whether to trust you with data.
Side by side
Both are attestation reports issued by licensed CPA firms. However, they answer different questions.
| SOC 1 | SOC 2 | |
|---|---|---|
| Focus | Controls relevant to financial reporting. | Security and the other trust criteria. |
| Main reader | The customer's financial auditor. | Security and procurement teams. |
| Typical services | Payroll, billing, claims, fund admin. | SaaS, hosting, data processing. |
| Types | Type 1 and Type 2. | Type 1 and Type 2. |
SOC 1 vs SOC 2: which fits you?
Tick what describes your service. Mostly ticks suggest SOC 2.
Your result appears here as you tick, so you can see what is still open.
How to tell which one is meant
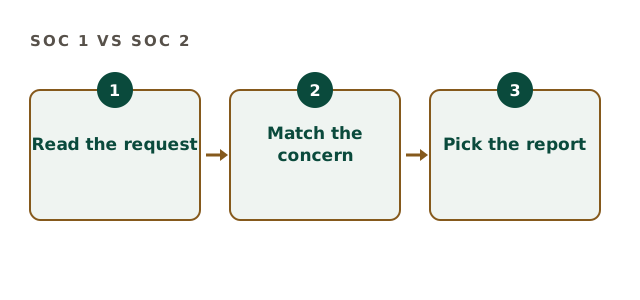
Read the request carefully. For example, a finance team asking about controls over transactions usually means SOC 1. However, a vendor security questionnaire almost always means SOC 2. If unsure, ask in writing, because the wrong report wastes months.
When you need both
Some services touch both money and data, such as payroll software. Therefore some companies produce both reports, often with the same CPA firm and overlapping evidence. That is efficient, but scope each one clearly.
Where we help in SOC 1 vs SOC 2 decisions
We prepare companies for SOC 2. So if a customer actually needs SOC 1, we say so plainly rather than selling the wrong work. The examination itself is always performed by a licensed, independent CPA firm. Reference: AICPA guidance on SOC 2.
A quick example makes it concrete. A payroll provider changes how much each employee is paid, so its customers' financial auditors care about its controls; that points to SOC 1. However, the same provider also stores bank details and identity documents, so security teams may ask for SOC 2 as well. When both concerns exist, ask each requester which report they will actually read, because finance and security teams rarely read the same document.
SOC 1 vs SOC 2 questions
Is SOC 2 better than SOC 1?
Neither is better. They answer different questions, so pick the one your customer needs.
Can one CPA firm do both?
Yes. Many firms issue both, often with shared evidence.
Which is more common for SaaS in SOC 1 vs SOC 2?
SOC 2, because SaaS buyers mostly ask about data protection.
What about SOC 3?
SOC 3 is a public summary of a SOC 2, which has its own guide.
Related guides
Not sure which report you need?
Send us the customer's request. We tell you plainly which report it describes, then scope the preparation.
Scope your preparation