Comparison
ISO 27001 vs SOC 2: choosing the one your buyers expect
The ISO 27001 vs SOC 2 decision is mostly about where your customers are. US buyers usually ask for SOC 2, while European and international buyers often ask for ISO 27001.
- Preparation, not the examination
- A licensed CPA firm signs the report
- Plain-English guidance
The basic difference in ISO 27001 vs SOC 2
ISO 27001 is a certifiable standard for an information security management system. So you receive a certificate from an accredited certification body. SOC 2, by contrast, is an attestation report from a licensed CPA firm, and there is no SOC 2 certificate.
Side by side
Both show a serious security programme. However, they work differently.
| ISO 27001 | SOC 2 | |
|---|---|---|
| Output | Certificate. | Attestation report. |
| Issued by | Accredited certification body. | Licensed CPA firm. |
| Common with | European and international buyers. | US buyers. |
| Focus | Management system and risk process. | Controls against trust criteria. |
| Cycle | Three-year certificate with yearly audits. | Yearly report. |
ISO 27001 vs SOC 2: quick decision check
Tick what applies. Mostly ticks point to SOC 2 first.
Your result appears here as you tick, so you can see what is still open.
How much the two overlap
Many controls overlap, such as access control, logging and vendor review. Therefore doing one first makes the second much faster. However, ISO 27001 also requires management system elements, such as internal audit and management review.
Which one to do first
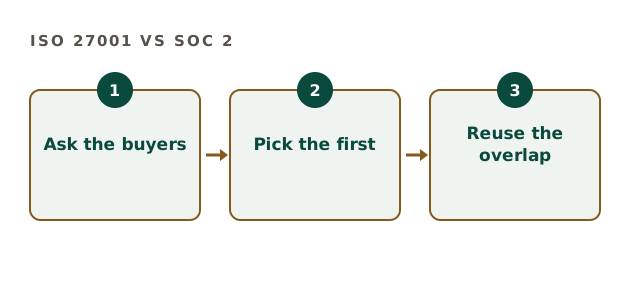
Look at your pipeline. If most deals are in the US, start with SOC 2. But if most are in Europe, start with ISO/IEC 27001. Also ask your largest prospects directly, because one large deal often decides it.
Our role in ISO 27001 vs SOC 2
We prepare companies for the SOC 2 examination. So if ISO 27001 is the better first step for you, we say so. The SOC 2 examination is always performed by a licensed CPA firm. Reference: AICPA guidance on SOC 2.
Timing also matters. ISO 27001 certification needs an internal audit and a management review before the certification audit, so plan for those steps. A SOC 2 Type 2, by contrast, needs its watch period. Therefore both take months, but for different reasons. If a large deal depends on one of them, work backwards from the buyer's deadline before choosing, because the faster path is not always the obvious one.
ISO 27001 vs SOC 2 questions
Is ISO 27001 vs SOC 2 an either-or choice?
Not long term. Many companies hold both, reusing shared controls.
Which is cheaper?
It depends on scope. However, doing the second after the first is always cheaper.
Does ISO 27001 replace SOC 2 for US buyers?
Sometimes, but many US buyers still ask specifically for SOC 2.
Is there a SOC 2 certificate like ISO?
No. SOC 2 is an attestation, not a certification.
Related guides
Decided on SOC 2 first?
Tell us your timeline and size. We reply with a written scope and a fixed preparation fee.
Scope your preparation