Guide
Salesforce SOC 2 compliance: their report, your org
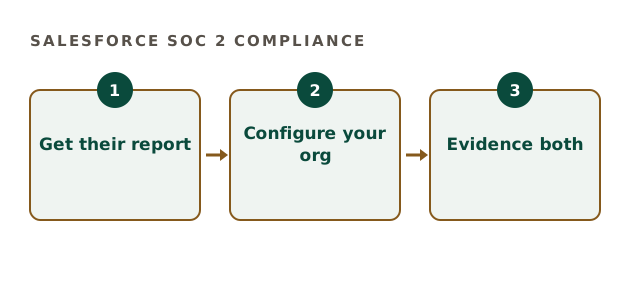
Salesforce SOC 2 compliance has two halves. Salesforce evidences its platform controls, while your own org configuration remains part of your SOC 2 scope.
- Preparation, not the examination
- A licensed CPA firm signs the report
- Plain-English guidance
What Salesforce SOC 2 compliance covers on their side
Salesforce publishes compliance documentation for its services. So customers can obtain reports covering the platform's controls for vendor reviews.
However, the report describes Salesforce's controls. It says nothing about how your team configured profiles, sharing or integrations.
What Salesforce SOC 2 compliance leaves to you
Most real risk sits in configuration. For example, broad permission sets or forgotten connected apps.
| Area | Your responsibility |
|---|---|
| Access | Profiles, permission sets and reviews |
| Authentication | MFA and single sign-on |
| Integrations | Connected apps and their scopes |
| Change | Sandbox testing and approved deployments |
| Data | Exports, sharing rules and retention |
Salesforce SOC 2 compliance check
Tick what is true for your org.
Your result appears here as you tick, so you can see what is still open.
Evidence for Salesforce SOC 2 compliance
Your CPA firm samples changes and access, wherever they happen. Therefore Salesforce admin changes need the same discipline as code changes.
- Access review records for Salesforce users
- Deployment records from sandbox to production
- Connected app inventory
- Setup audit trail exports
Common gaps
Admins often change production directly. Because Salesforce makes that easy, change management evidence goes missing. Also, integrations keep wide access long after projects end.
In addition, check which data leaves Salesforce through reports and exports.
Where Clearpoint helps
We bring Salesforce into your control set and evidence routine. Our preparation fee is fixed, between $5,000 and $40,000. We are not a CPA firm. Salesforce documentation is on the Salesforce Trust site.
Also review integrations whenever a new tool connects. Because each connected app holds a token, a forgotten integration can keep wide access long after anyone uses it. So the connected app inventory deserves its own periodic review. In addition, limit who can install apps, because that keeps the inventory short. As a result, Salesforce evidence stays clean between examinations.
Salesforce SOC 2 compliance questions
Does Salesforce SOC 2 compliance cover our org?
No. It covers the platform, while your configuration stays in your scope.
Where do we get Salesforce SOC 2 compliance documents?
Through Salesforce's compliance and trust resources, as a customer.
Is Salesforce SOC 2 compliance evidence needed every year?
Yes. Review the latest report each period.
Do admin changes count as changes?
Yes. The CPA firm treats them like any production change.
Related guides
Bring Salesforce SOC 2 compliance into your scope
Tell us how your team uses Salesforce. We reply with a written scope and a fixed preparation fee. Also mention how many admins you have, because admin access drives most of the evidence work.
Scope your preparation