Guide
GitHub SOC2: their report, and the evidence in your repositories
GitHub SOC2 questions come in two forms. Some teams want GitHub's own report for vendor review, while others want to know how GitHub supports their own examination.
- Preparation, not the examination
- A licensed CPA firm signs the report
- Plain-English guidance
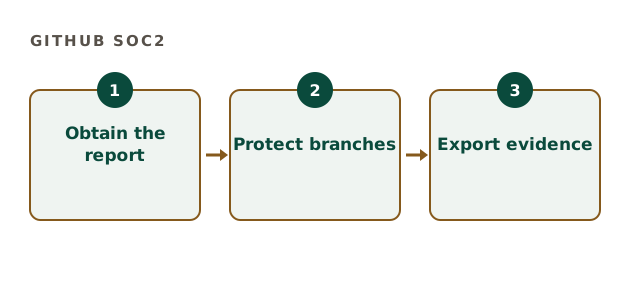
Getting the GitHub SOC2 report
GitHub makes compliance reports available to customers through its trust and enterprise resources. Also, access is usually tied to a paid organisation or enterprise account.
Note the period covered. So your vendor file shows current evidence.
How GitHub SOC2 evidence supports change management
For many software companies, GitHub is the change management system. Therefore its settings become core evidence.
| Setting | Control it supports |
|---|---|
| Branch protection on main | Changes cannot skip review |
| Required pull request approvals | Peer review before merge |
| Status checks | Tests pass before deploy |
| Single sign-on | Access tied to identity |
GitHub SOC2 readiness check
Tick what your organisation enforces.
Your result appears here as you tick, so you can see what is still open.
Access control in GitHub SOC2 scope
Access reviews apply to repositories too. For example, former contractors with write access are a classic exception.
- Organisation members reviewed periodically
- Outside collaborators approved and removed promptly
- Admin rights limited
- Deploy keys and tokens inventoried
Exporting evidence
The CPA firm samples merged changes. So keep a way to show, for each sampled change, the pull request, approvals and checks. As a result, sampling takes minutes.
In addition, document emergency merges, because they always get questions.
Where Clearpoint helps
We configure repository controls with your engineers and set up evidence exports. Our preparation fee is fixed, between $5,000 and $40,000. We are not a CPA firm. GitHub's material is on the GitHub security page.
Also review personal access tokens and machine users. Because they often bypass single sign-on, they can undermine access control quietly. So inventory them, assign owners and remove unused ones. In addition, restrict who can change branch protection, because a single admin change can switch off the control. As a result, the evidence stays trustworthy across the whole period.
GitHub SOC2 questions
Does GitHub SOC2 status make our code compliant?
No. GitHub's report covers its service, while your settings remain yours.
Which GitHub SOC2 settings matter most?
Branch protection, required reviews and single sign-on.
How do we obtain the GitHub SOC2 report?
Through GitHub's trust and enterprise resources, as a customer.
Do emergency merges fail the control?
Not if they follow a documented, approved process.
Related guides
Turn GitHub SOC2 settings into clean evidence
Tell us how your team ships code. We reply with a written scope and a fixed preparation fee. Also mention how many repositories are in scope, because that shapes the evidence plan. So the estimate is realistic from the start.
Scope your preparation