Guide
The SOC 1 Type 2 report, and when you need one instead of SOC 2
A SOC 1 Type 2 report shows how well a service organisation's controls over financial reporting worked across a period. So it serves your customers' auditors, rather than their security teams.
- Preparation, not the examination
- A licensed CPA firm signs the report
- Plain-English guidance
What a SOC 1 Type 2 report covers
SOC 1 focuses on controls relevant to your customers' financial statements. For example, payroll processing, claims handling or billing services.
The Type 2 version tests whether those controls operated effectively over a period. Therefore it carries more weight than a point-in-time Type 1.
SOC 1 Type 2 report compared with SOC 2
The two reports answer different questions. However, buyers sometimes ask for the wrong one.
| Topic | SOC 1 | SOC 2 |
|---|---|---|
| Focus | Financial reporting controls | Security and related criteria |
| Main readers | Customers' financial auditors | Customers' security and vendor teams |
| Framework | Control objectives you define | AICPA Trust Services Criteria |
SOC 1 Type 2 report readiness check
Tick what applies to your service.
Your result appears here as you tick, so you can see what is still open.
Who needs a SOC 1 Type 2 report
If your service affects how customers record money, their auditors may ask for one. Also, public company customers often need it for their own control obligations.
- Payroll and benefits providers
- Billing and payments processors
- Loan or claims servicers
- Fund administrators
How the process runs
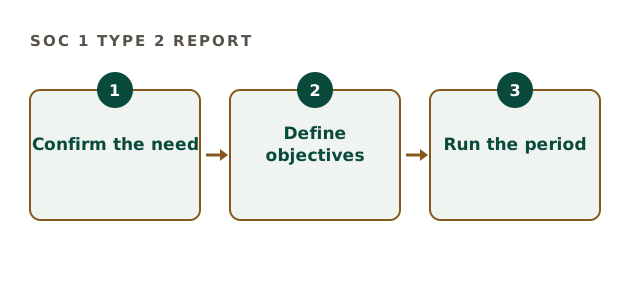
You define control objectives and the controls that meet them. Then a licensed CPA firm tests them across the period. As a result, the report describes both design and operating effectiveness.
In addition, many companies need both SOC 1 and SOC 2. Shared controls, such as access management, can serve both examinations.
Where Clearpoint helps
Our focus is SOC 2 preparation. However, we help clients decide whether SOC 1 is the right report, and we prepare shared controls. We are not a CPA firm, so a licensed firm issues any report. Background is on the AICPA guidance on SOC 2 page.
Also confirm the request in writing. Because customers sometimes say SOC 1 when they mean SOC 2, a short email to their auditor or vendor team avoids months of wasted work. So the report you commission answers the question they actually asked. In addition, ask which period they need covered, because it decides when testing can start.
SOC 1 Type 2 report questions
Who issues a SOC 1 Type 2 report?
A licensed, independent CPA firm.
Can a SOC 1 Type 2 report replace SOC 2?
Usually not. Security teams generally want SOC 2.
How long is a SOC 1 Type 2 report period?
Commonly six to twelve months, as agreed with the CPA firm.
Do we need both reports?
Some providers do, when customers need both financial and security assurance.
Related guides
Decide whether you need a SOC 1 Type 2 report
Tell us what your customers asked for. We reply with a written view and, where it fits, a fixed preparation fee.
Scope your preparation